 To strengthen its information security protection and management, the Company has appointed an Information Security Officer (ISO) and dedicated information security personnel. In addition, the roles and responsibilities of the dedicated information security unit have been incorporated into the Company's Internal Control System.
I. Information Security Management Framework
- Information Office is responsible for establishing information security policies, and regularly reviews and revises operating standards to ensure compliance with security requirements
- Internal Audit Office incorporates the information security process into its annual audit plan
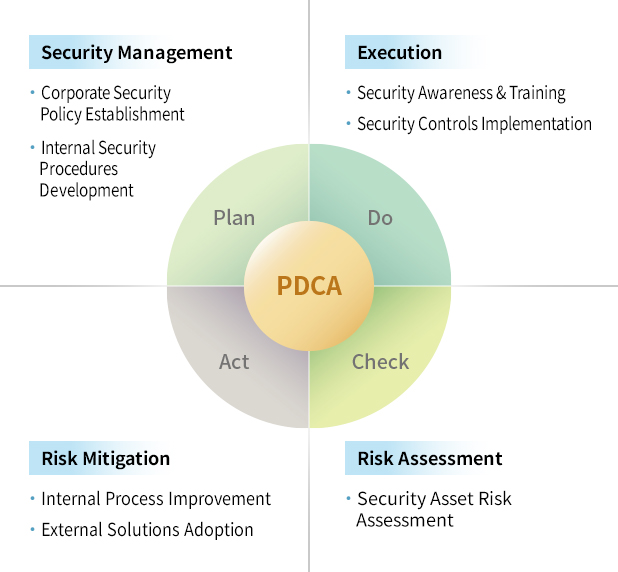
- Managed using the PDCA (Plan-Do-Check-Act) approach to ensure goal achievement and continuous improvement
Information Security Management
1. Policy and Procedure Development
- Establish information security policies
- Develop internal information security procedures
2. Implementation and Promotion
- Conduct information security awareness and employee training
- Implement information security control measures
3. Risk Mitigation and Improvement
- Continuously improve internal procedures
- Introduce external cybersecurity solutions
4. Risk Assessment
- Conduct information asset risk assessments
II. Information Security Management Policy
Policies and Procedures
Establish and implement an Information Security Management Policy to regulate employees' information security practices and operational conduct.
Process Management
Follow the information processing procedures defined in the Company's Internal Control System to ensure effective implementation of information security management processes.
Information Security Monitoring
Deploy firewall protection to prevent malicious cyberattacks and continuously monitor internal and external network activities for anomalies, thereby establishing a comprehensive information security defense mechanism.
Employee Awareness and Training
Cybersecurity awareness is promoted through periodic postings on the Company's Enterprise Employee Portal (EIP) e-bulletin board. Information security education is also reinforced during onboarding training for new employeesI.
III. Information Security Management Measures
| Item |
Management Measures |
|
Firewall Protection
|
Firewall access control, connection approval procedures, and traffic monitoring |
|
Internet Access Control
|
Restricted access to social media, gaming, and file-sharing websites |
| Antivirus Protection |
Centrally managed antivirus software with automatic signature updates |
| System Access Management |
Role-based access control for systems and applications |
| Email Security |
Anti-virus, anti-spam, and malicious email detection mechanisms |
| Website Protection |
Firewall protection against external cyberattacks |
| Data Backup |
Full and differential backups for servers and databases |
| Data Center Management |
Restricted access, environmental controls, fire protection, and UPS support |
| File Storage Management |
Centralized storage and backup of critical files on NAS server |
| Security Self-Assessment |
Quarterly information security inspections and reviews |
| Risk Assessment |
Annual cybersecurity risk assessment and improvement plans |
IV. Information Security Training and Resource Investment
- Appointed 1 Chief Information Security Officer and 1 dedicated information security personnel.
- Conducted 5 information security meetings in 2025.
- Organized 4 information security training sessions with 321 total participants.
- Continued investment in information security governance, risk management, and regulatory compliance, aiming to minimize the potential impact of security incidents on company operations and information assets.
V. Information Security Risk Management
- Established an information security incident reporting and response mechanism.
- Regularly review and remediate system, application, and network vulnerabilities.
- Implement account and password management controls, including password strength requirements and deactivation of accounts for departed employees or those with role changes, to prevent unauthorized access.
- Apply data classification and access control for critical and sensitive information, based on data sensitivity and importance, to ensure the legality, security, and integrity of data use.
- Report information security management performance to the Board of Directors annually. The latest report was presented on March 10, 2026.